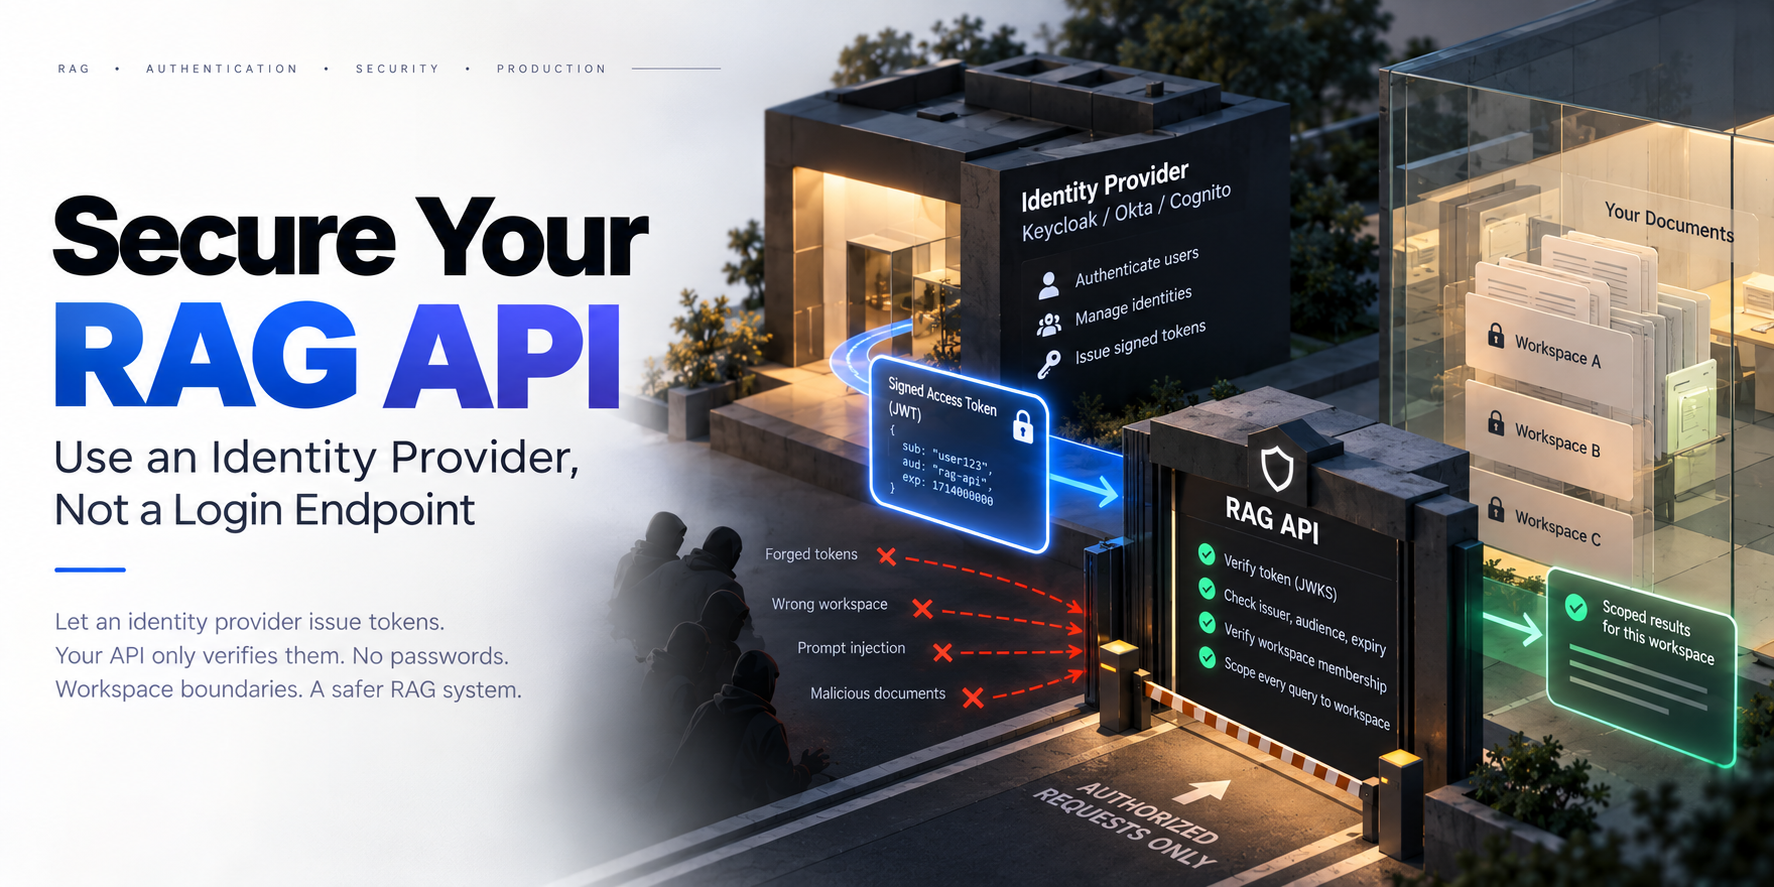
Secure a RAG API without minting tokens or storing passwords
An identity provider issues the tokens, the API only verifies them, and neither the model nor an uploaded PDF gets a say in who the user is.
Series
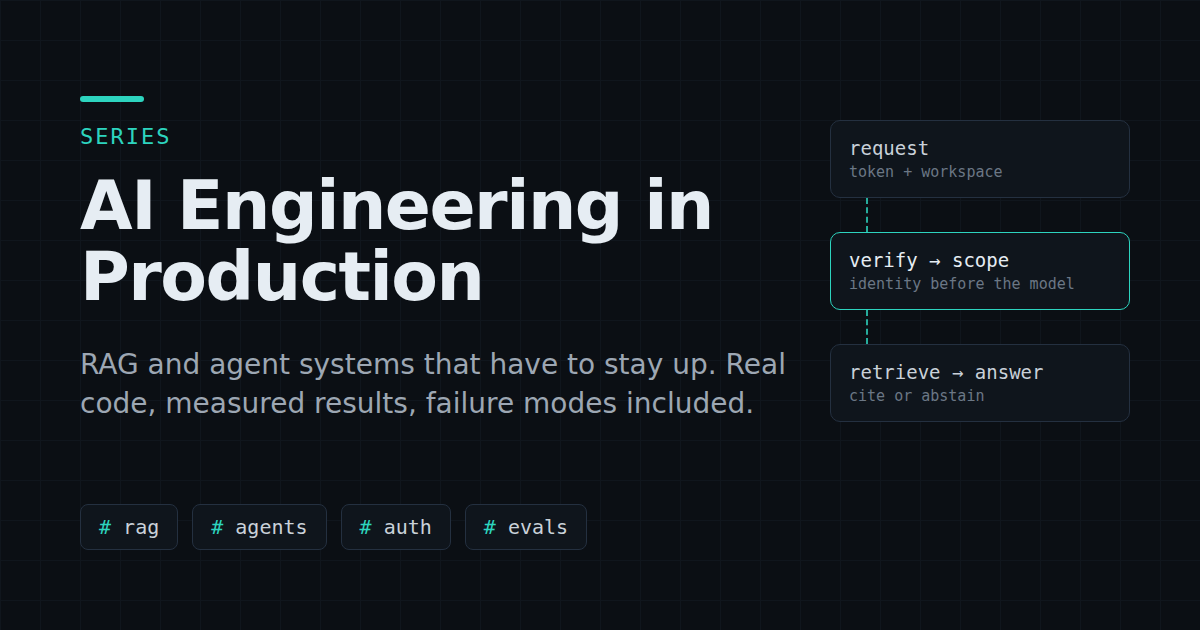
Production RAG and agent systems that have to stay up: auth, retrieval, agents with brakes, evaluation and observability. Every post comes from a system I actually built and measured, and I only keep the complicated piece when a simpler one loses on a real metric.
An identity provider issues the tokens, the API only verifies them, and neither the model nor an uploaded PDF gets a say in who the user is.
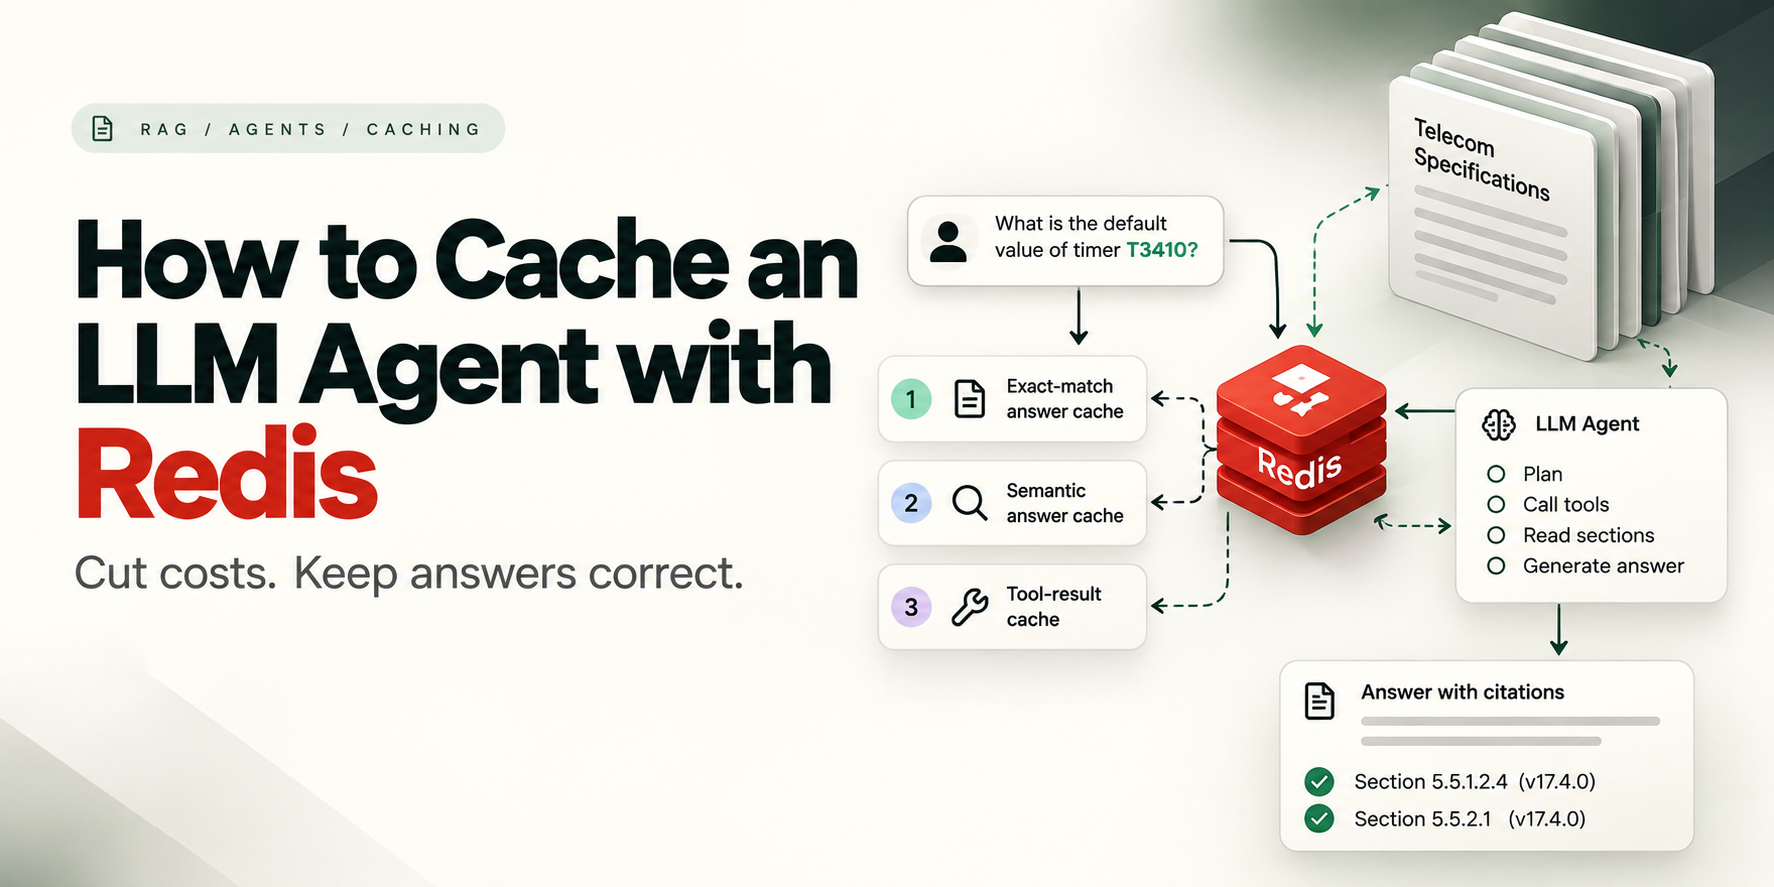
Three caches in front of an agentic RAG system, and five cases where a cache hit must be treated as a miss
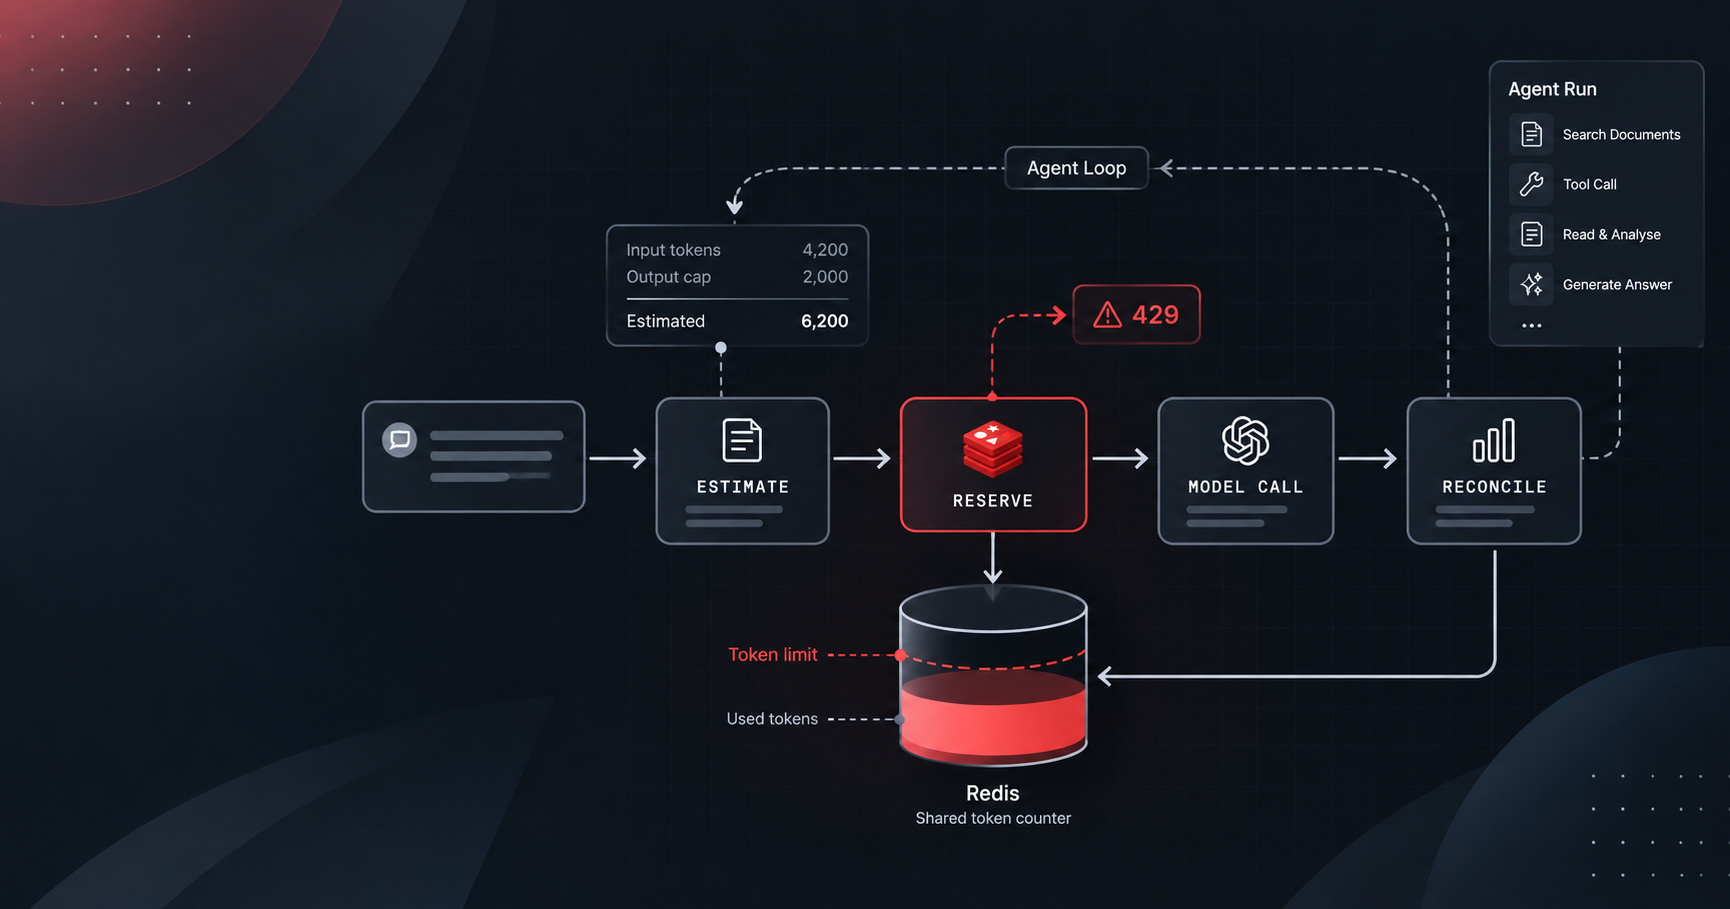
Reserve an estimate before the model call, correct it after, and give every agent to run its own budget.
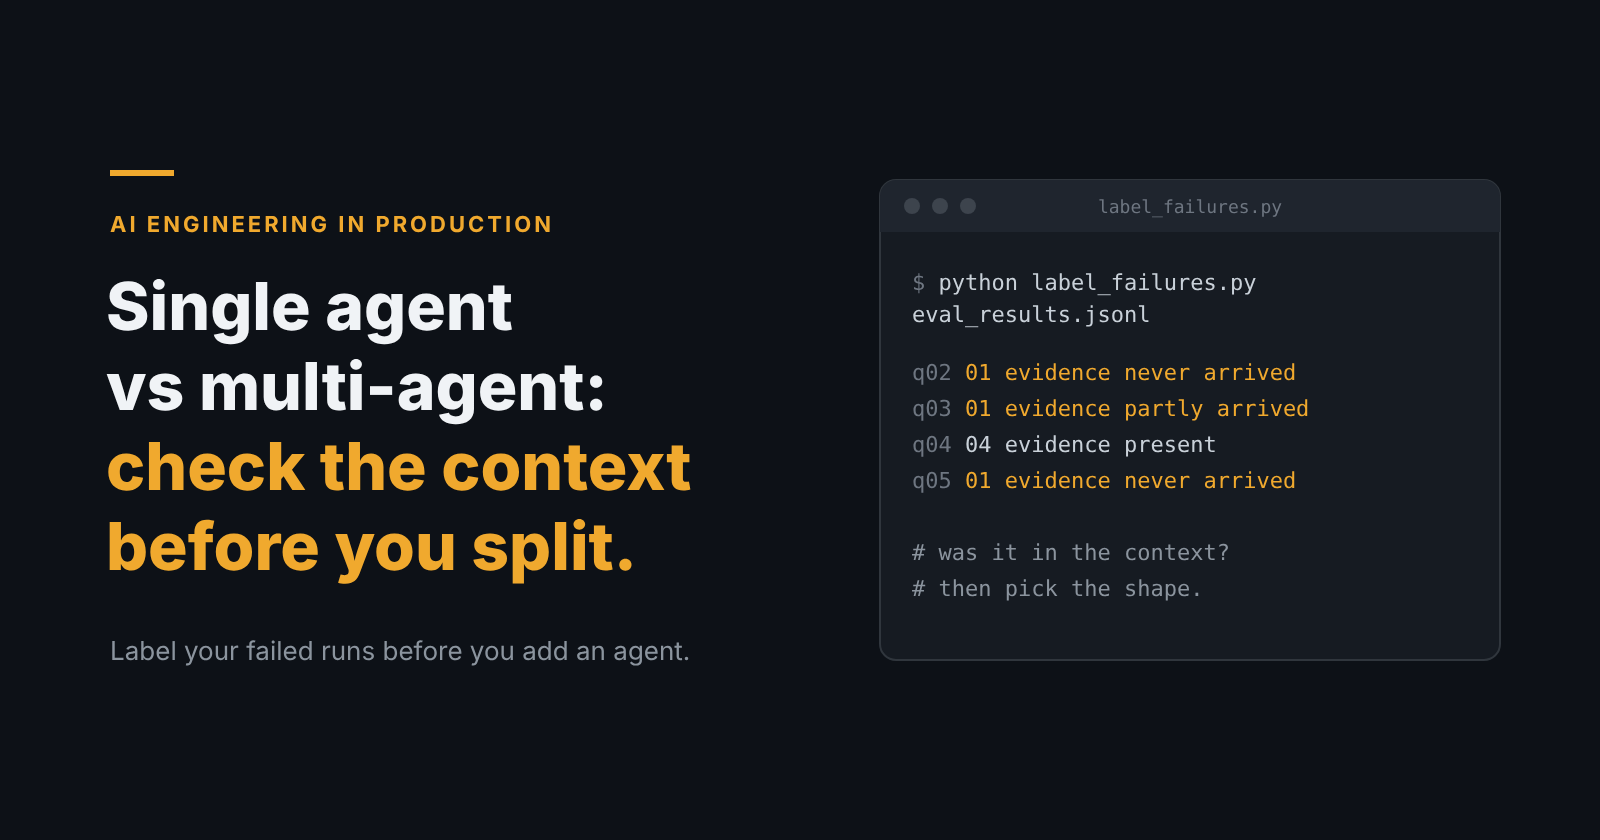
In my RAG eval, [X] of [N] failures never had the evidence in context. A second agent would have failed the same way at about 4x the tokens.
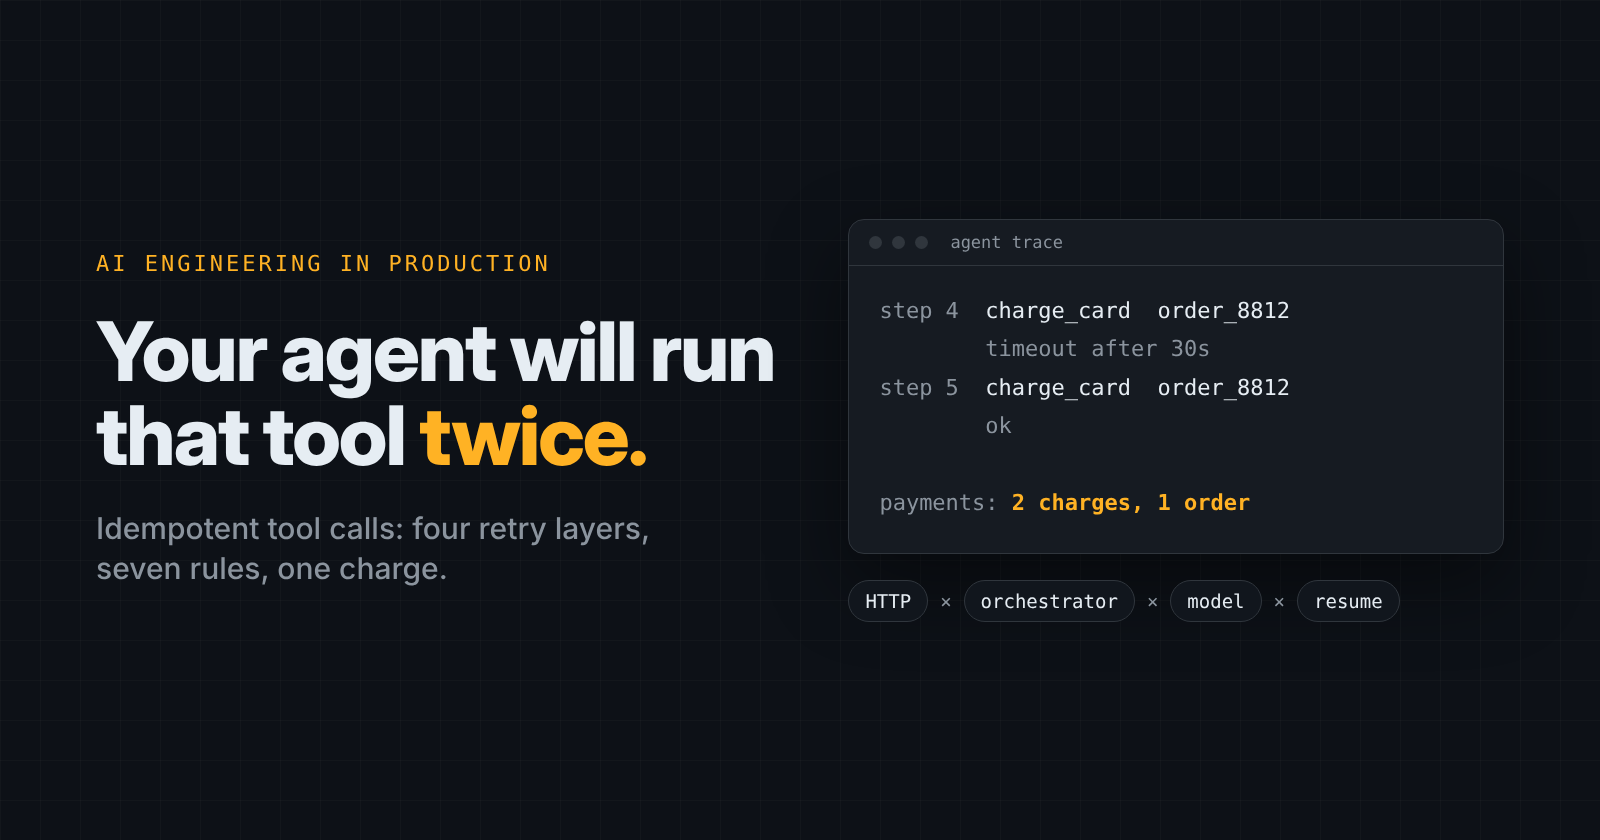
Retries come from four layers and can multiply to 18 runs of one action. Seven rules make a dangerous tool call happen exactly once.
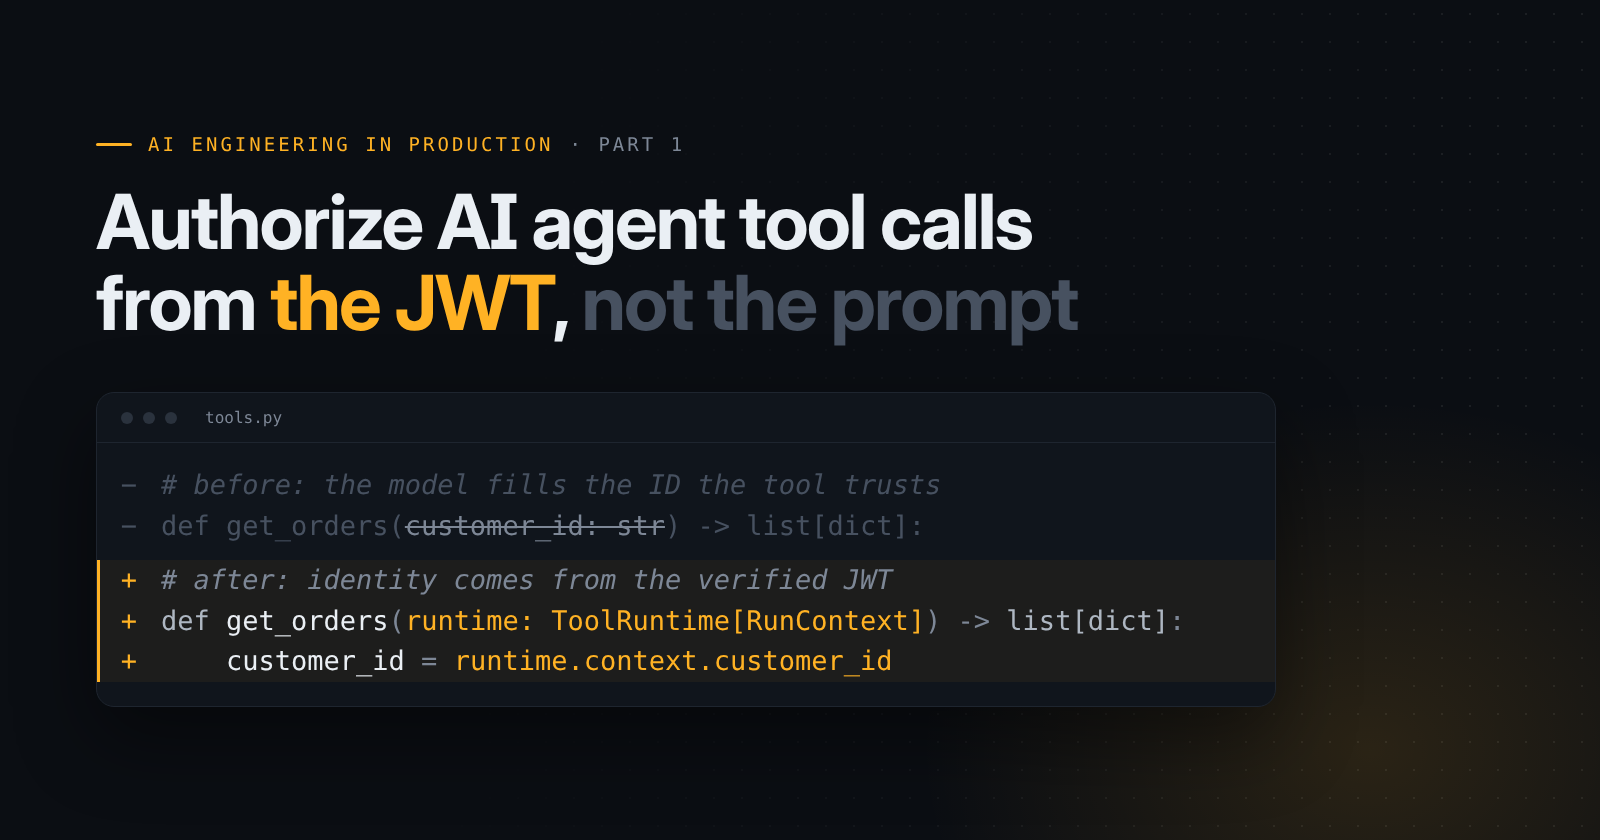
The JWT was valid. The model still picked the customer ID. Move identity into the state so a fooled model can't reach the wrong data.